Cache-Control Header Generator: Build Bulletproof Caching Headers in Minutes
Learn how the free Cache-Control Header Generator composes max-age, s-maxage, immutable and stale-while-revalidate directives, then exports ready-to-paste nginx, Apache and Express.js snippets.
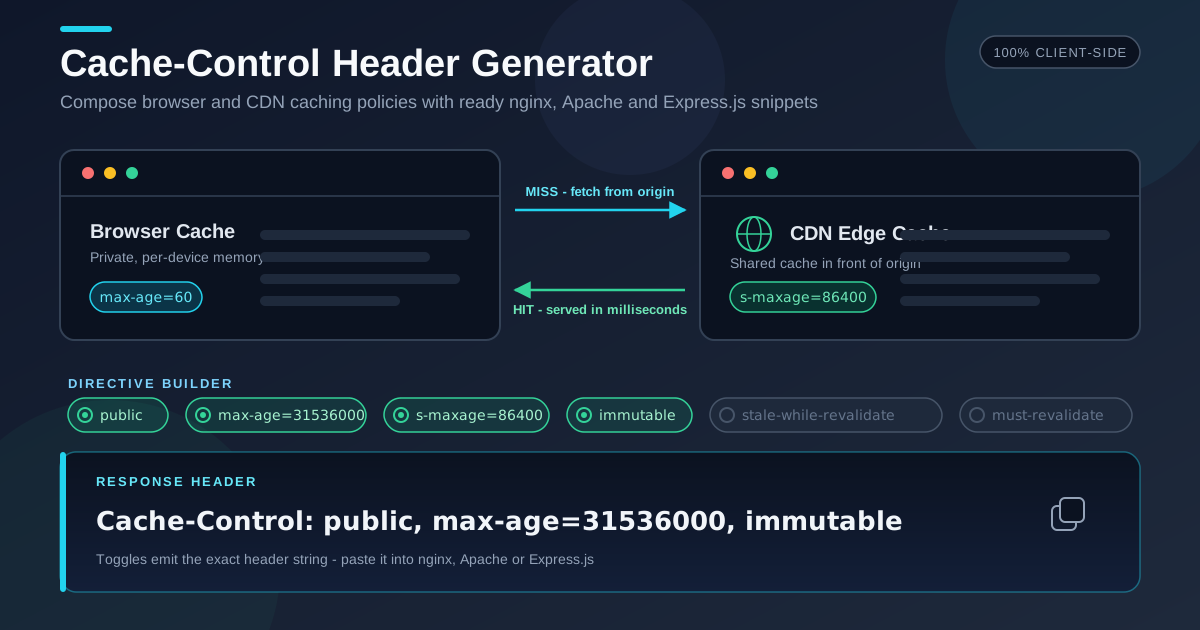
Table of Contents
Cache-Control Header Generator: Build Bulletproof Caching Headers in Minutes
Caching is the biggest performance lever you can pull without touching application code. A well-tuned Cache-Control header turns a 300 ms origin round trip into a near-instant response served from the browser's own memory, and cuts your CDN egress bill at the same time. Yet the syntax is unforgiving: one misplaced comma, or one confused choice between no-cache and no-store, and you either ship stale content to users or hammer your servers with requests that never needed to leave the browser.
The Cache-Control Header Generator removes the guesswork. Instead of memorizing RFC 7234 semantics, you flip a set of clear toggles — public versus private, max-age, s-maxage, immutable, stale-while-revalidate, stale-if-error, must-revalidate and more — and watch the exact header string compose itself in real time. When you are happy with the result, the tool hands you ready-to-paste snippets for nginx, Apache, and Express.js, so the policy you design is the policy you deploy. Everything runs 100% client-side.
This guide explains how to use the tool, which directives genuinely matter in production, and three proven recipes for hashed assets, HTML documents, and JSON APIs.
Why Use the Cache-Control Header Generator?
- Zero syntax errors. Order, comma placement, and value formats are handled for you, so the header you copy is always valid HTTP.
- Learn while you build. Each toggle maps to a real RFC directive, so you absorb caching semantics instead of copying mystery configs.
- Server-agnostic output. The same policy renders as an nginx add_header block, an Apache Header set directive, and Express.js middleware.
- Full modern directive set. You get s-maxage, immutable, stale-while-revalidate, stale-if-error, must-revalidate, and proxy-revalidate — the directives that separate a good CDN setup from a great one.
- Instant what-if testing. Compare a 60-second policy against a one-year immutable one by flipping a single toggle.
- Private and free. Everything computes in your browser: no accounts, no uploads, no limits.
Key Features
| Feature | What It Does |
|---|---|
| Toggle/directive builder | Switch public, private, no-cache, no-store, max-age, s-maxage, must-revalidate, proxy-revalidate, immutable, stale-while-revalidate and stale-if-error on or off |
| Live header preview | The composed Cache-Control string updates as you toggle, ready to copy |
| nginx snippet | Emits an add_header block for a server or location context |
| Apache snippet | Emits a Header set line for .htaccess or vhost configuration |
| Express.js snippet | Emits middleware that sets the header on matching responses |
| 100% client-side | Nothing is sent to a server; the tool works offline once loaded |
Three details make the output especially practical:
- Snippets mirror the header exactly, so what you preview is what your server emits.
- Values are editable, from max-age=31536000 for hashed bundles to max-age=0 for always-revalidate HTML.
- Directives cover both browser and CDN layers, so one pass yields a coherent policy instead of two conflicting ones.
How to Use the Tool Step by Step
- Open the tool. Head to the Cache-Control Header Generator — no signup required.
- Choose the audience. Pick public if CDNs may cache the response, private if it is user-specific, or no-store for sensitive responses that must never be cached anywhere.
- Set freshness. Enter max-age for browsers and s-maxage for the shared cache. These are seconds: 60 a minute, 86400 a day, 31536000 a year.
- Add safety directives. Toggle must-revalidate to forbid stale serving after expiry, immutable for hashed assets, and stale-while-revalidate or stale-if-error for resilience during revalidation or origin outages.
- Copy the output. Review the live header string, paste the nginx, Apache, or Express.js snippet into your config, and deploy.
The Directives That Actually Matter
Caching happens in two distinct places, and understanding the split is the key to every good policy.
Browser Cache vs Shared CDN Cache
The browser cache is private to one device; the CDN (shared) cache is shared by every user hitting that edge node — and each layer has its own directive. max-age=60 tells browsers to reuse the response for sixty seconds; s-maxage=600 tells shared caches to keep it for ten minutes, and it wins over max-age wherever a shared cache stores the response. Setting them independently lets HTML live briefly on the CDN while browsers treat it as always-fresh.
immutable for Hashed Assets
immutable tells the browser the resource will never change during its freshness lifetime, so it skips even conditional revalidation requests. Paired with a content hash in the filename (like app.a8f3d2.js) and max-age=31536000, a returning visitor loads the bundle straight from disk with zero network chatter. Never use it on a URL whose content can change — that is exactly what causes "I deployed but users still see the old site" bugs.
stale-while-revalidate and stale-if-error
stale-while-revalidate=86400 adds an async grace window: when a cached response expires, the cache serves the stale copy immediately and refreshes in the background. stale-if-error=604800 extends the idea to failures — if the origin returns a 5xx or times out, the cache keeps serving its stale copy instead of an error page. Together they are the cheapest resilience upgrade for static-heavy sites.
no-cache vs no-store
These are constantly confused. no-cache means "store this, but revalidate before every use" — the response still benefits from cheap 304 Not Modified round trips. no-store means "do not persist this anywhere" — the right choice for banking pages, personalized exports, and anything under authentication.
must-revalidate
Once a must-revalidate response goes stale, caches may not serve it — they must revalidate and may return a 504 if the origin is unreachable. Use it when stale content is worse than no content, such as price or inventory data. Pair max-age=0, must-revalidate when you want browser caching without ever risking staleness.
Three Recipes That Cover 95% of Sites
Hashed static assets. Long TTL plus immutability:
add_header Cache-Control "public, max-age=31536000, immutable";
HTML documents. Revalidate on every navigation, with a CDN grace window:
Header set Cache-Control "no-cache, s-maxage=60, stale-while-revalidate=300"
API JSON. Keep personal responses out of shared caches:
app.use('/api/me', (req, res, next) => {
  res.set('Cache-Control', 'private, no-store');
  next();
});
Practical Use Cases
Static Asset Pipelines
Bundlers like webpack, Vite, and Next.js fingerprint every JS and CSS file. Serve those hashed files with public, max-age=31536000, immutable and repeat visitors' load time collapses to nearly zero while your CDN offload ratio climbs above 95%. Generate the snippets once and standardize the policy across staging and production.
Single-Page Application Deployments
SPAs need a split policy: index.html must always be fresh, because it references the hashed bundles by URL, while the bundles themselves can be cached for a year. Use no-cache on the HTML, a short s-maxage so the CDN absorbs revalidation traffic, and immutable on assets. Miss this split and you get the classic white-screen deploy bug.
API Responses
Public GET endpoints benefit from public, s-maxage=300, stale-while-revalidate=600 — the CDN answers most requests and your database barely notices traffic spikes. Personalized or authenticated endpoints must send private, no-store so intermediaries never store user data.
Fixing Stale-Deploy Bugs
When users see an old version after a deploy, the culprit is almost always a long max-age on HTML or a hashed asset served without immutable. Compose the correct split policy, redeploy the headers, and the bug disappears as caches roll over — no cache-busting query strings required.
Best Practices for Production Caching
- Hash filenames before granting long TTLs. max-age=31536000, immutable is only safe when the URL changes whenever the content does.
- Test with curl -I after every deploy. Inspect the actual header from your servers and CDN; configs get overridden somewhere in the chain.
- Remember CDNs can override your headers. Many platforms impose defaults or respect only s-maxage.
- Define one policy per resource class. Assets, HTML, and APIs each deserve their own rule set; a global header is how stale-deploy bugs are born.
- Prefer no-cache over no-store for HTML. You keep freshness guarantees while making 304 round trips cheap.
- Add stale-if-error as cheap insurance. One directive keeps your site up through origin outages.
Speed Up Your Site Today
Point your team at the Cache-Control Header Generator, pick the recipe that matches each resource class, and paste the generated snippet into your server config. Ten minutes of header work routinely beats a week of micro-optimizing JavaScript.
Related Tools You Might Like:
- Security Headers Generator — build CSP, HSTS, and other protective headers with the same toggle approach.
- HSTS Header Generator — craft Strict-Transport-Security policies that force HTTPS across your domain.
- htaccess Generator — produce Apache .htaccess files that bundle caching with redirects and other rules.
Happy caching!
Frequently Asked Questions
Q: What is the difference between max-age and s-maxage?
A: max-age controls how long any cache — including the browser — may reuse a response. s-maxage applies only to shared caches like CDNs and overrides max-age there, letting the edge hold content longer than devices.
Q: When should I use no-cache instead of no-store?
A: Use no-cache when content must be revalidated before every use but can still be stored, keeping 304 Not Modified responses fast and cheap. Use no-store only for sensitive responses that must never be persisted by any cache.
Q: Is immutable safe to use on all my assets?
A: Only on URLs whose filenames contain a content hash or version that changes whenever the file changes. Adding it to a stable URL like /styles.css causes browsers to keep using an outdated file until the TTL expires.
Q: Does stale-while-revalidate slow down the first visitor after expiry?
A: No. The cache answers immediately with the stale copy and fetches fresh content in the background, so the first visitor still gets the fastest possible response.
Q: Will my CDN respect the headers the tool generates?
A: Most major CDNs respect Cache-Control and prioritize s-maxage, but some platforms apply their own defaults. Verify with curl -I against your production domain and check your provider's documentation.